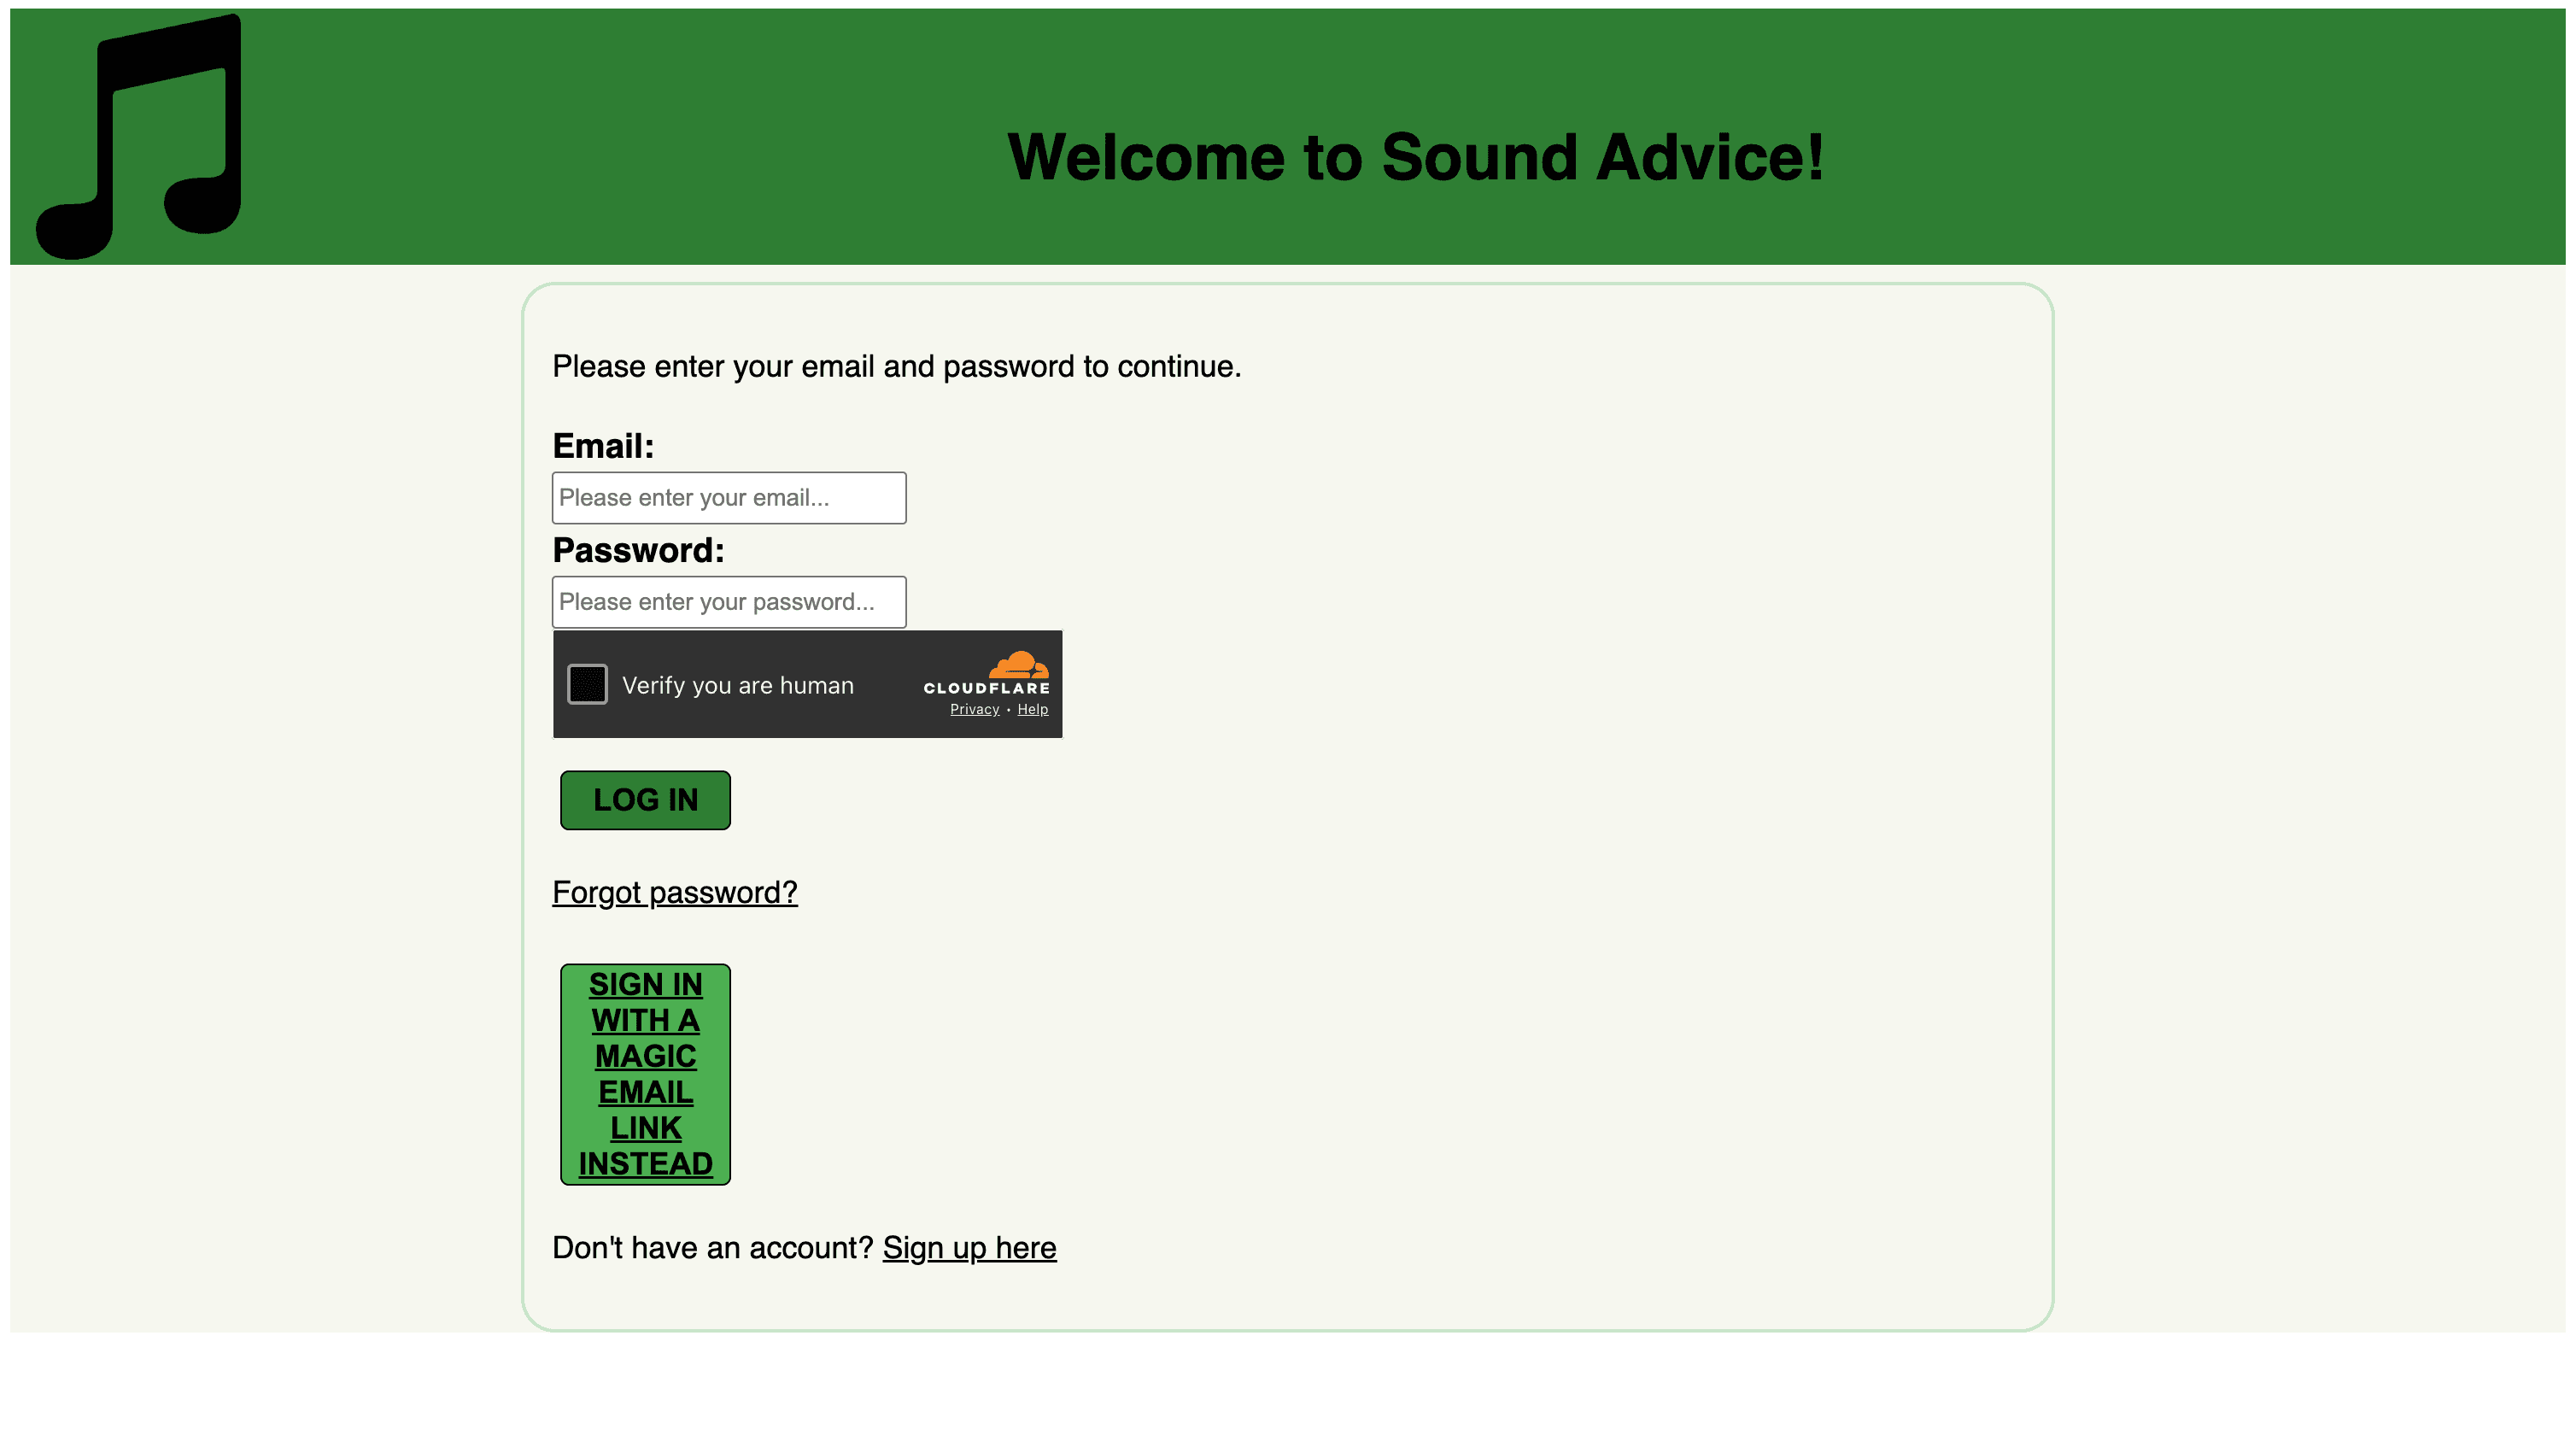
SoundAdvice is a music advice forum where users help each other improve. Anyone can post a question, and an admin approves it before it goes public so the quality stays high. The forum itself isn't really the point: it needs accounts, roles, sessions, user-submitted HTML and file uploads, which makes it a realistic thing to attack.
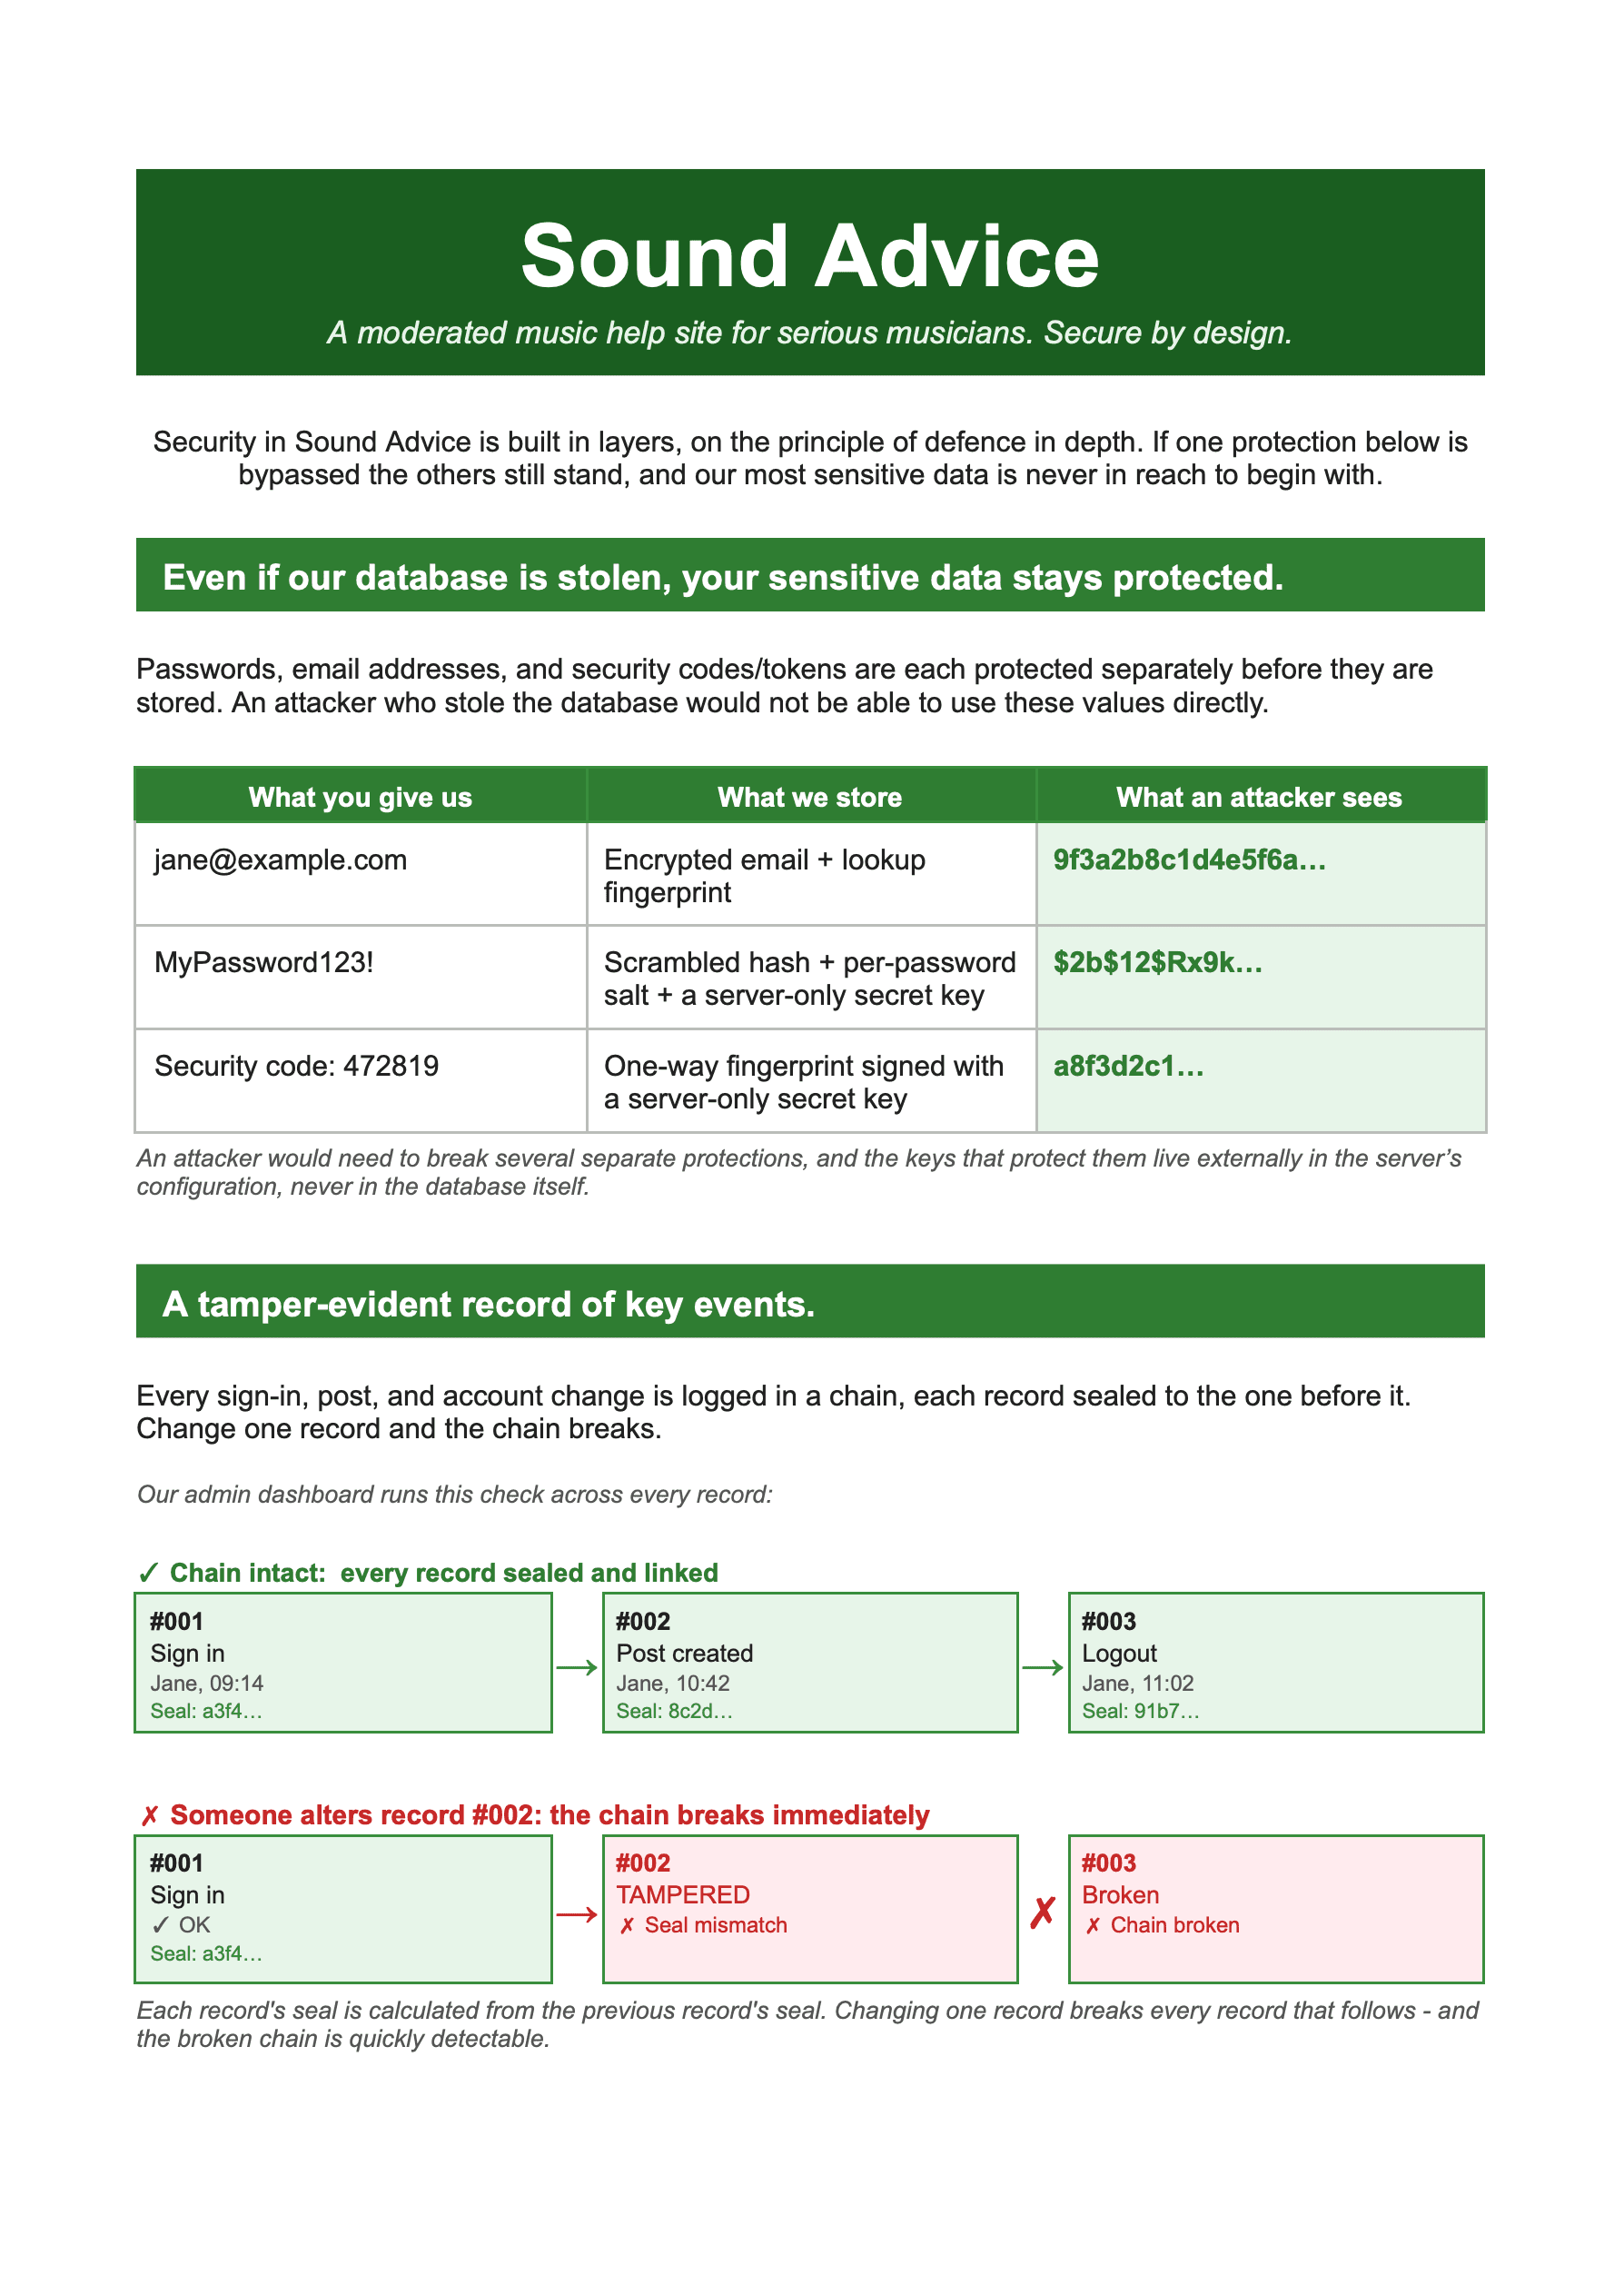
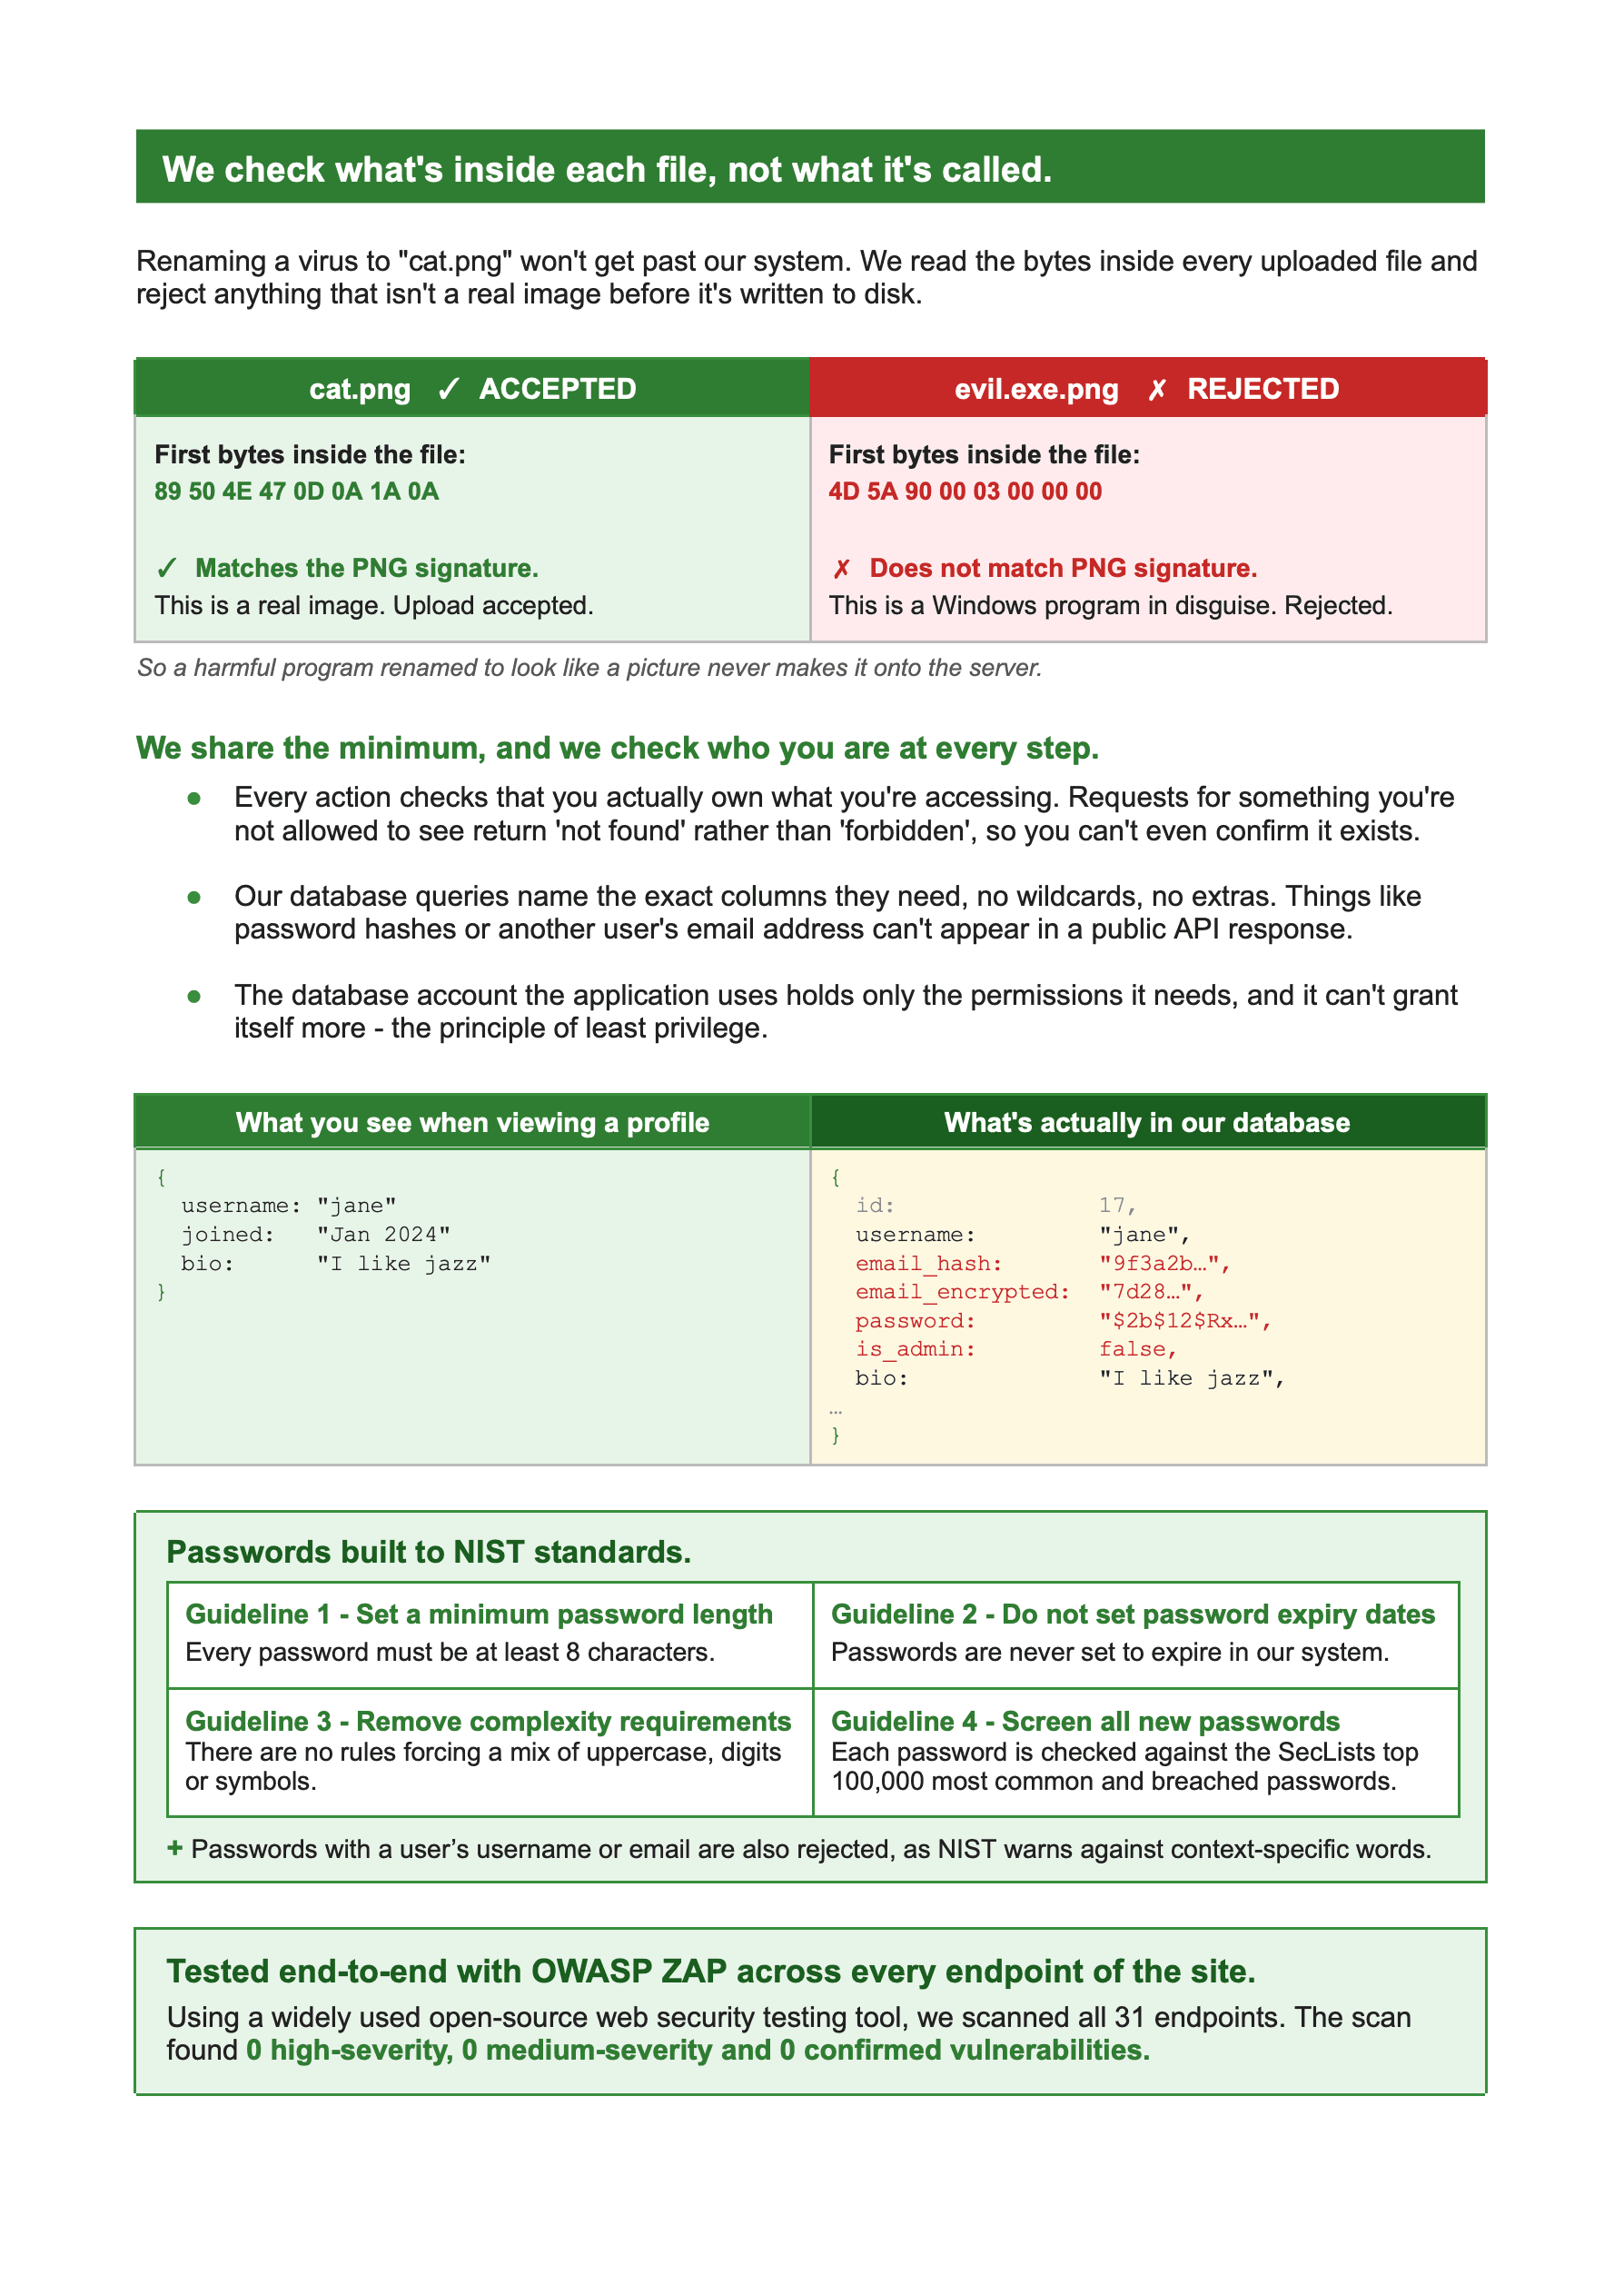
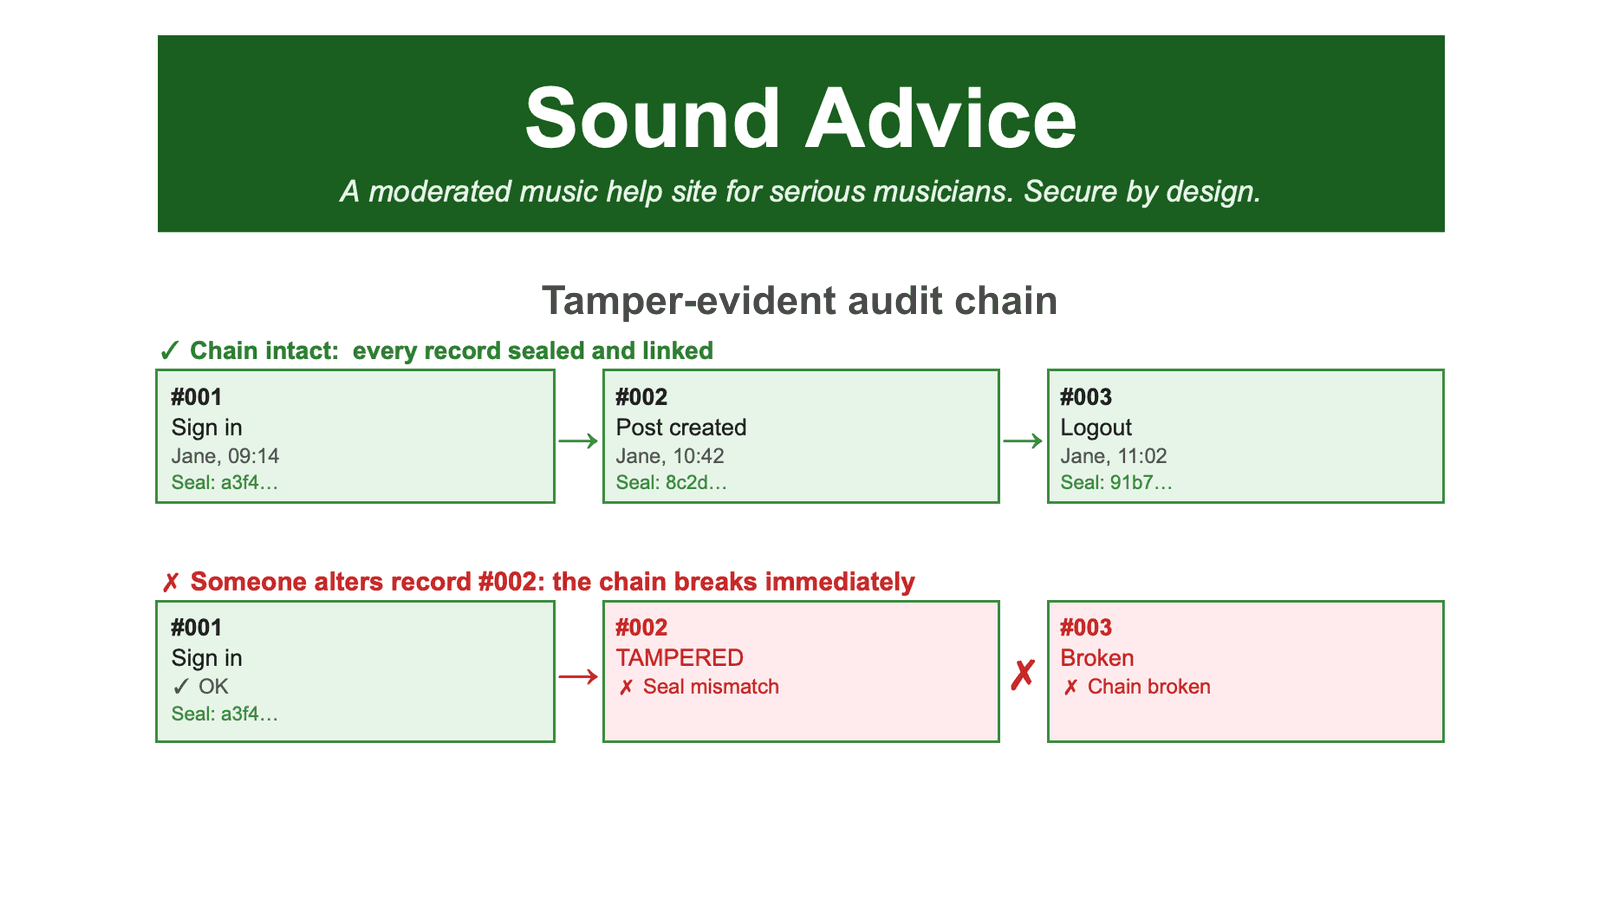
Every security control in it is hand-written. The whole thing runs on four packages: express, pg, bcrypt and dotenv. Sessions, CSRF tokens, the HTML sanitiser, the multipart file parser, rate limiting, password screening, encrypted email storage with a searchable lookup index, and a hash-chained audit log are all built on Node's standard library.
In a real product most of that would come from a library, but the point was to build each control and then try to break it, which is hard to do when the mechanism is hidden behind someone else's API. SoundAdvice was built by a team of three, and the work went into the backend and the threat model, not the interface.
This page is only an introduction. The README is where the project is actually documented, with every security control and the evidence behind it.
Read the full write-up on GitHub